

Microsoft SC-401 Real Exam Questions Test Engine Dumps Training With 275 Questions
SC-401 Actual Questions Answers PDF 100% Cover Real Exam Questions
Microsoft SC-401 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 95
You have a Microsoft 365 E5 subscription that uses Microsoft Purview.
You are evaluating the use of custom data assessment scans to identify the potential oversharing of data in the subscription.
What is the maximum number of items the data assessments can support per location?
- A. 50.000
- B. 100.000
- C. 200.000
- D. 500.000
Answer: C
Explanation:
Comprehensive Detailed Explanation with References
Custom Data Access Governance (DAG) data assessment scans in Microsoft Purview can be run on selected SharePoint Online or OneDrive locations to check for oversharing and exposure. Each custom assessment scan supports up to 200,000 items per location. This cap is documented in Microsoft's guidance for custom data access governance assessments.
NEW QUESTION # 96
Hotspot Question
You have a Microsoft 365 subscription that contains the users shown in the following table.
You create the data loss prevention (DLP) policies shown in the following table.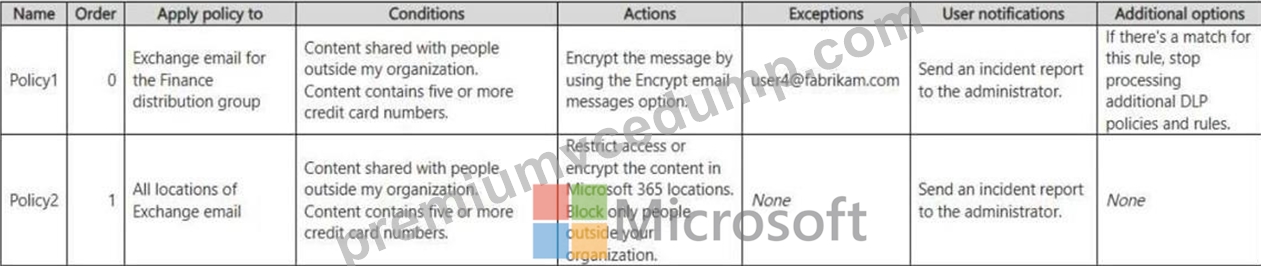
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: No
Policy1 will be applied. Policy1 has an exception for user4@fabrikam. The processing is stopped at Policy1.
Note: Data loss prevention (DLP) policies are processed in a specific order. This process is called policy precedence. The policy with the lowest priority number is processed first. The first rule is configured as a priority "0" by default, the next one as "1", and so on.
Conditions are inclusive and are where you define what you want the rule to look for and context in which those items are being used.
Box 2: Yes
Policy1 will be applied.
Box 3: No
Policy2 will be applied.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/dlp-policy-reference
NEW QUESTION # 97
You create a retention label that has a retention period of seven years.
You need to ensure that documents containing a credit card number are retained for seven years.
Other documents must not be retained.
What should you create?
- A. a retention policy that deletes files automatically
- B. a retention policy that retains files automatically
- C. a retention label policy of type auto-apply
- D. a retention label policy of type publish
Answer: C
Explanation:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-retention-labels-automatically
NEW QUESTION # 98
Hotspot Question
You have a Microsoft 365 tenant named contoso.com that contains two users named User1 and User2. The tenant uses Microsoft Purview Message Encryption.
User1 plans to send emails that contain attachments as shown in the following table.
User2 plans to send emails that contain attachments as shown in the following table.
For which emails will the attachments be encrypted? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Mail3 only
Box 2: Mail4 and Mail6 only
Reference:
https://support.microsoft.com/en-gb/office/introduction-to-irm-for-email-messages-bb643d33-4a3f-
4ac7-9770-fd50d95f58dc?ui=en-us&rs=en-gb&ad=gb#FileTypesforIRM
https://docs.microsoft.com/en-us/microsoft-365/compliance/ome?view=o365-worldwide
https://docs.microsoft.com/en-us/office365/servicedescriptions/exchange-online-service- description/exchange-online-limits#message-limits-1
NEW QUESTION # 99
Hotspot Question
You have a new Microsoft 365 E5 tenant.
You need to create a custom trainable classifier that will detect product order forms. The solution must use the principle of least privilege.
What should you do first? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
The opt-in can't be performed by the Compliance Administrator, the GA is required:
"To access classifiers in the UI:
the Global admin needs to opt in for the tenant to create custom classifiers.
Compliance Administrator role is required to train a classifier."
https://learn.microsoft.com/en-us/microsoft-365/compliance/classifier-get-started- with?view=o365-worldwide
NEW QUESTION # 100
Hotspot Question
You have a Microsoft 365 E5 tenant that contains a trainable classifier named Classifier1.
You need to increase the accuracy of Classifier1. The solution must use the principle of least privilege.
Which feature should you use and to which role group should you be added? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Content Explorer
Increase classifier accuracy
Classifiers, like sensitive information types (SIT) and trainable classifiers are used in various kinds of policies to identify sensitive information. Like most such models, sometimes they identify an item as being sensitive that isn't. Or, they may not identify an item as being sensitive when it actually is. These are called false positives and false negatives.
Box 2: Compliance data administrator
Permissions
In order to get access to the content explorer tab, an account must be assigned membership in any one of these roles or role groups.
Microsoft 365 role groups
Global administrator
Compliance administrator
Security administrator
*-> Compliance data administrator
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/data-classification-increase-accuracy
https://learn.microsoft.com/en-us/microsoft-365/compliance/data-classification-content-explorer
NEW QUESTION # 101
Hotspot Question
You have a Microsoft 365 E5 subscription that uses Microsoft Purview and just-in-time (JIT) protection. Fallback action in case of failure is set to Block users from completing actions.
The subscription contains the users shown in the following table.
The subscription contains the devices shown in the following table.
The devices contain the files shown in the following table.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Yes
User1 is included in the JIT protection scope.
File1.docx has the file classification evaluation status of not evaluated, and is located on Device1.
Device1 is onboarded.
JIT will block the action.
Note: In a Microsoft 365 environment with Purview and Just-in-Time (JIT) protection, a file with a
"not evaluated" classification status will be protected by JIT. When JIT protection is enabled, Endpoint DLP will block all egress activities on monitored files while waiting for policy evaluation to complete, including when the evaluation status is "not evaluated".
Box 2: No
User2 is not within the JIT protection scope.
Box 3: No
User3 is included in the JIT protection scope.
File3.docx has the file classification evaluation status of not evaluated, and is located on Device3.
Device3 is not onbarded.
Reference:
https://learn.microsoft.com/en-us/purview/endpoint-dlp-get-started-jit
NEW QUESTION # 102
You have a Microsoft 365 £5 subscription.
You are implementing insider risk management.
You need to create an insider risk management notice template and format the message body of the notice template.
How should you configure the template? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Step 1 - Where to configure Insider Risk Management notices
Insider risk management notices are part of the Microsoft Purview Insider Risk Management solution.
They are created and managed within the Microsoft Purview compliance portal.
The Microsoft 365 admin center, Microsoft Defender portal, or Microsoft Entra admin center are not used for notice templates.
Therefore, the correct choice for the portal is: Microsoft Purview portal.
Step 2 - Supported formats for notice templates
When creating an Insider Risk Management notice template, Microsoft Purview allows customization of the message body in HTML format.
HTML provides rich text formatting (fonts, colors, links, branding).
Markdown, RTF, and XML are not supported options for Purview notice templates.
Therefore, the correct format is: HTML.
Step 3 - Microsoft Reference
Microsoft documentation states:
"Notice templates are created and managed in the Microsoft Purview compliance portal. The body of the notice message is authored in HTML format to allow for full customization." Reference: Create insider risk management notice templates in Microsoft Purview
NEW QUESTION # 103
You need to be alerted when users share sensitive documents from Microsoft OneDrive to any users outside your company.
What should you do?
- A. From the Microsoft Purview portal create an insider risk policy
- B. From the Microsoft Defender portal, create an activity policy.
- C. From the Microsoft Purview portal, start a data investigation.
- D. From the Microsoft Defender portal create a file policy
Answer: D
Explanation:
An activity policy in Microsoft Defender for Cloud Apps (Microsoft Defender portal) allows you to track and alert on specific user actions, such as sharing sensitive documents externally from OneDrive. This policy can detect file-sharing activities and send alerts when files are shared with external users, which meets the requirement.
NEW QUESTION # 104
You have a Microsoft 565 E5 subscription.
You plan to use Microsoft Purview insider risk management.
You need to create an insider risk management policy that will detect data theft from Microsoft SharePoint Online by users that submitted their resignation or are near their employment termination date.
What should you do first?
- A. Configure Office indicators.
- B. Configure a Physical badging connector.
- C. Onboard devices to Microsoft Defender for Endpoint.
- D. Configure a HR data connector.
Answer: D
NEW QUESTION # 105
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1.
Site1 contains the files shown in the following table.
In the Microsoft Purview portal, you create a content search named Conlent1 and configure the search conditions as shown in the following exhibit.
Which files will be returned by Content1?
- A. File3.docx only
- B. File1 .docx, File2.docx, and File3.docx
- C. File2.docx only
- D. File1.docx and File2.docx only
- E. File1 .docx and File3.docx only
Answer: A
NEW QUESTION # 106
You have a Microsoft 365 E5 subscription.
You need to prevent users from uploading data loss prevention (DLP)-protected documents to the following third-party websites:
# web1.contoso.com
# web2.contoso.com
The solution must minimize administrative effort.
To what should you set the Service domains setting for Endpoint DLP?
- A. web*.contoso.com
- B. web1.contoso.com and web2.contoso.com
- C. contoso.com
- D. *.contoso.com
Answer: B
Explanation:
The Service domains setting in Microsoft 365 Endpoint Data Loss Prevention (Endpoint DLP) allows administrators to block or allow specific domains for file uploads. The goal is to prevent users from uploading DLP-protected documents to web1.contoso.com and web2.contoso.com.
Setting the Service domains to "web1.contoso.com and web2.contoso.com" precisely targets the two specific third-party websites, minimizing administrative effort while ensuring strict control.
NEW QUESTION # 107
You have a Microsoft 365 E5 subscription that uses Microsoft Purview insider risk management and contains three users named User1, User2, and User3.
All insider risk management policies have adaptive protection enabled and the default conditions for insider risk levels configured.
The users perform the following activities, which trigger insider risk policy alerts:
* User1 performs at least one data exfiltration activity that results in a high severity risk score.
* User2 performs at least three risky user activities within seven days, that each results in a high severity risk score.
* User3 performs at least bwo data exfiltration activities within seven days, that each results in a high severity risk score.
Which insider risk level is assigned to each user? To answer, drag the appropriate levels to the correct users.
Each level may be used once, more than once, or not at all. You may need to drag the split bar between panes or seroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 108
You have a Microsoft 36S subscription that contains the sensitive information types (SITs) shown in the following exhibit.
Use the drop-down menus To select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct flection is worth one point.
Answer:
Explanation:
Explanation:
Step 1 - Understanding the scenario
The screenshot shows multiple Sensitive Information Types (SITs) in Microsoft Purview, including:
ABA Routing Number (Microsoft-built)
ASP.NET Machine Key (Microsoft-built)
Adatum document patterns (custom, Fingerprint type)
Adatum numbers (custom, Entity type)
Bundled SITs (like All Credential Types, All Full Names)
The question is asking:
Which SITs can you copy to create a new SIT?
Which SITs can you edit directly without copying?
Step 2 - Microsoft rules for SITs
Built-in SITs (published by Microsoft Corporation):
These cannot be edited directly. To modify them, you must create a copy first.
Custom SITs (created in your tenant, e.g., Contoso):
These can be edited directly without making a copy.
Reference: Create a custom sensitive information type
Step 3 - Apply to the exhibit
"Adatum numbers" is published by Contoso (the organization), so it is a custom SIT. This means it can be edited directly.
All SITs, whether built-in or custom, can be copied to form a new SIT.
NEW QUESTION # 109
Case Study 1 - Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Existing Environment
Microsoft 365 Environment
Contoso has a Microsoft 365 E5 tenant. The tenant contains the administrative user accounts shown in the following table.
Users store data in the following locations:
- SharePoint sites
- OneDrive accounts
- Exchange email
- Exchange public folders
- Teams chats
- Teams channel messages
When users in the research department create documents, they must add a 10-digit project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1, Site2, Site3, and Site4.
Site2 contains the files shown in the following table.
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Site3 stores documents related to the company's projects. The documents are organized in a folder hierarchy based on the project.
Site4 has the following two retention policies applied:
- Name: Site4RetentionPolicy1
Locations to apply the policy: Site4
Delete items older than: 2 years
Delete content based on: When items were created
- Name: Site4RetentionPolicy2
Locations to apply the policy: Site4
Retain items for a specific period: 4 years
Start the retention period based on: When items were created
At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research department documents were leaked.
Requirements
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
- Name: DLPpolicy1
Locations to apply the policy: Site2
Conditions:
Content contains any of these sensitive info types: SWIFT Code
- Instance count: 2 to any
Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
- All administrative users must be able to review DLP reports.
- Whenever possible, the principle of least privilege must be used.
- For all users, all Microsoft 365 data must be retained for at least
one year.
- Confidential documents must be detected and protected by using
Microsoft 365.
- Site1 documents that include credit card numbers must be labeled
automatically.
- All administrative users must be able to create Microsoft 365
sensitivity labels.
- After a project is complete, the documents in Site3 that relate to
the project must be retained for 10 years.
Drag and Drop Question
You need to meet the technical requirements for the Site1 documents.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
Create a retention label. -> Has nothing to do with information protection.
Create a sensitive info type. -> Not needed because for credit cards, there is a built-in one.
NEW QUESTION # 110
You are implementing Microsoft Purview Advanced Message Encryption for a Microsoft 365 tenant named contoso.com You need to meet the following requirements:
* All email to a domain named (abrikam.com must be encrypted automatically.
* Encrypted emails must expire seven days after they are sent
What should you configure for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Requirement 1 - Encrypt all email to fabrikam.com automatically
To force encryption for mail sent to a specific external domain (fabrikam.com):
You configure a mail flow rule (transport rule) in the Exchange admin center (EAC).
This rule can apply Office Message Encryption (OME) automatically when messages match conditions such as recipient domain.
Reference: Define mail flow rules to encrypt email messages
Correct choice: A mail flow rule in the Exchange admin center
Requirement 2 - Encrypted emails must expire after 7 days
To configure expiration and access control over encrypted emails:
You use Microsoft Purview sensitivity labels with encryption settings.
A label policy in the Purview portal can enforce encryption, set access rights, and define expiration (e.g., revoke access after 7 days).
Sensitive info types or mail flow rules cannot configure expiration.
Reference: Configure encryption settings for sensitivity labels
Correct choice: A label policy in the Microsoft Purview portal
NEW QUESTION # 111
......
PremiumVCEDump SC-401 Exam Practice Test Questions: https://www.premiumvcedump.com/Microsoft/valid-SC-401-premium-vce-exam-dumps.html
SC-401 Exam questions and answers: https://drive.google.com/open?id=1-lvKSVwiQlqkmcOaHaAhhjb6YXFZoAc4