

[May 03, 2026] Genuine SPLK-5001 Exam Dumps Free Demo
Printable & Easy to Use Cybersecurity Defense Analyst SPLK-5001 Dumps 100% Same Q&A In Your Real Exam
Splunk SPLK-5001 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 57
The eval SPL expression supports many types of functions. Which of these function categories is not valid with eval?
- A. Threat functions
- B. Comparison and Conditional functions
- C. Text functions
- D. JSON functions
Answer: A
NEW QUESTION # 58
A Risk Rule generates events on Suspicious Cloud Share Activity and regularly contributes to confirmed incidents from Risk Notables. An analyst realizes the raw logs these events are generated from contain information which helps them determine what might be malicious.
What should they ask their engineer for to make their analysis easier?
- A. Allowlist more events based on this information.
- B. Create another detection for this information.
- C. Add this information to the risk message.
- D. Create a field extraction for this information.
Answer: D
NEW QUESTION # 59
Rotating encryption keys after a security incident is most closely linked to which security concept?
- A. Confidentiality
- B. Integrity
- C. Obfuscation
- D. Availability
Answer: A
NEW QUESTION # 60
An analyst investigates an IDS alert and confirms suspicious traffic to a known malicious IP. What Enterprise Security data model would they use to investigate which process initiated the network connection?
- A. Authentication
- B. Web
- C. Network traffic
- D. Endpoint
Answer: D
NEW QUESTION # 61
Which of the following use cases is best suited to be a Splunk SOAR Playbook?
- A. Visualizing complex datasets.
- B. Creating persistent field extractions.
- C. Taking containment action on a compromised host
- D. Forming hypothesis for Threat Hunting
Answer: C
NEW QUESTION # 62
There are different metrics that can be used to provide insights into SOC operations. If Mean Time to Respond is defined as the total time it takes for an Analyst to disposition an event, what is the typical starting point for calculating this metric for a particular event?
- A. When a Notable Event is triggered.
- B. When the end users are notified about the issue.
- C. When the malicious event occurs.
- D. When the SOC Manager is informed of the issue.
Answer: A
NEW QUESTION # 63
What is the term for a model of normal network activity used to detect deviations?
- A. A time series.
- B. A cluster.
- C. A data model.
- D. A baseline.
Answer: D
NEW QUESTION # 64
What is the first phase of the Continuous Monitoring cycle?
- A. Respond and Recover
- B. Assess and Evaluate
- C. Define and Predict
- D. Monitor and Protect
Answer: C
NEW QUESTION # 65
How are Notable Events configured in Splunk Enterprise Security?
- A. Via an Adaptive Response Action in a regular search.
- B. Via an Adaptive Response Action in a correlation search.
- C. During an investigation.
- D. As part of an audit.
Answer: B
NEW QUESTION # 66
An analyst is not sure that all of the potential data sources at her company are being correctly or completely utilized by Splunk and Enterprise Security. Which of the following might she suggest using, in order to perform an analysis of the data types available and some of their potential security uses?
- A. SOAR
- B. Splunk ITSI
- C. Splunk Intelligence Management
- D. Security Essentials
Answer: D
NEW QUESTION # 67
Refer to the exibit.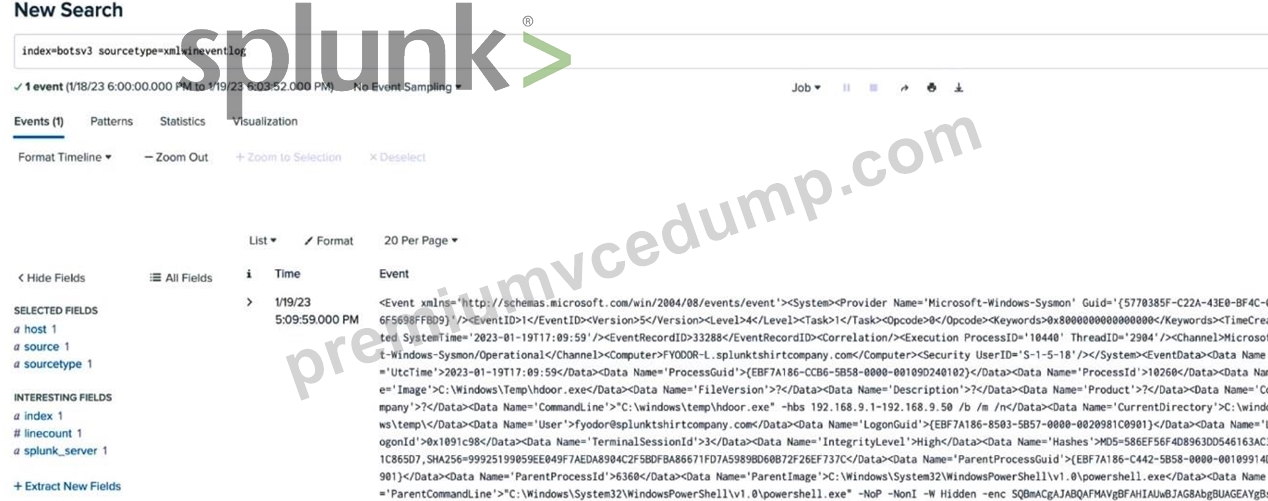
An analyst is building a search to examine Windows XML Event Logs, but the initial search is not returning any extracted fields. Based on the above image, what is themost likelycause?
- A. The analyst does not have the proper role to search this data.
- B. The analyst is searching newly indexed data that was improperly parsed.
- C. The analyst is not in the Drooer Search Mode and should switch to Smart or Verbose.
- D. The analyst did not add the excract command to their search pipeline.
Answer: C
NEW QUESTION # 68
Splunk SOAR uses what feature to automate security workflows so that analysts can spend more time performing analysis and investigation?
- A. Playbooks
- B. Adaptive Actions
- C. Workbooks
- D. Analytic Stories
Answer: A
NEW QUESTION # 69
An analyst is investigating how an attacker successfully performs a brute-force attack to gain a foothold into an organizations systems. In the course of the investigation the analyst determines that the reason no alerts were generated is because the detection searches were configured to run against Windows data only and excluding any Linux data.
This is an example of what?
- A. A True Negative.
- B. A True Positive.
- C. A False Positive.
- D. A False Negative.
Answer: D
NEW QUESTION # 70
Splunk Enterprise Security has numerous frameworks to create correlations, integrate threat intelligence, and provide a workflow for investigations. Which framework raises the threat profile of individuals or assets to allow identification of people or devices that perform an unusual amount of suspicious activities?
- A. Notable Event Framework
- B. Asset and Identity Framework
- C. Risk Framework
- D. Threat Intelligence Framework
Answer: C
NEW QUESTION # 71
While investigating findings in Enterprise Security, an analyst has identified a compromised device. Without leaving ES, what action could they take to run a sequence of containment activities on the compromised device that also updates the original finding?
- A. Run an adaptive response action that initiates a SOAR playbook.
- B. Run an event-level workflow action that initiates a SOAR playbook.
- C. Run an alert action that initiates a SOAR playbook.
- D. Run a field-level workflow action that initiates a SOAR playbook.
Answer: A
NEW QUESTION # 72
Enterprise Security has been configured to generate a Notable Event when a user has quickly authenticated from multiple locations between which travel would be impossible. This would be considered what kind of an anomaly?
- A. Identity Anomaly
- B. Access Anomaly
- C. Threat Anomaly
- D. Endpoint Anomaly
Answer: B
NEW QUESTION # 73
An analyst is attempting to investigate a Notable Event within Enterprise Security. Through the course of their investigation they determined that the logs and artifacts needed to investigate the alert are not available.
What event disposition should the analyst assign to the Notable Event?
- A. Benign Positive, since there was no evidence that the event actually occurred.
- B. Other, since a security engineer needs to ingest the required logs.
- C. True Positive, since there are no logs to prove that the event did not occur.
- D. False Negative, since there are no logs to prove the activity actually occurred.
Answer: B
NEW QUESTION # 74
......
SPLK-5001 Practice Test Give You First Time Success with 100% Money Back Guarantee!: https://www.premiumvcedump.com/Splunk/valid-SPLK-5001-premium-vce-exam-dumps.html
All Obstacles During SPLK-5001 Exam Preparation with SPLK-5001 Real Test Questions: https://drive.google.com/open?id=1OyHm9_4oVZrAet5VJhLD_yYbsqHzaU-q